New York, United States, October 20th, 2026, FinanceWire
Twelve minutes and forty-two seconds. That is how long it took one adversary, observed inside Amazon’s honeypot infrastructure, to move from a single vulnerability to complete control of everything the compromised systems could reach.
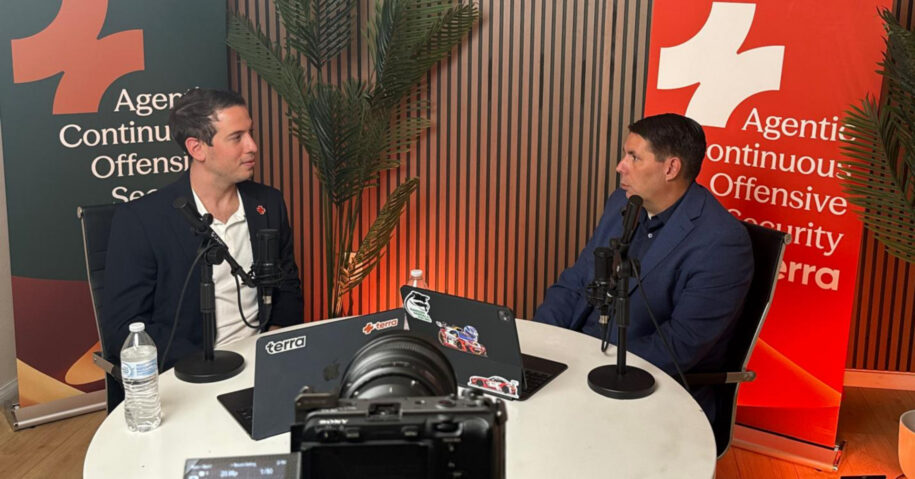
CJ Moses, CISO of Amazon, shared that figure on the first episode of the AI Native Cybersecurity Podcast, a new series from Terra Security hosted by the company’s co-founder and CEO, Shahar Peled. The number became a reference point for the entire conversation, which centered on a single technical reality: AI has compressed the attack timeline, and defenders now have to engineer for velocity.
The Clock Has Changed
The 12-minute sequence was not a simple break-in. The attacker gained access, performed reconnaissance to map every permission available, acted on each one, and then kept spreading outward into adjacent systems. In earlier years, that same chain would have unfolded as a campaign stretched across weeks or months.
Moses pointed out how quickly the industry’s assumptions have aged. “If you think of the whole paradigm of 30, 60, 90-day patching windows, that seems so old, but it really was only like six months ago that’s the mindset,” he said. With adversaries using Mythos and comparable tools to both discover and weaponize flaws, the gap between disclosure and exploitation now shrinks to seconds.
When Peled suggested the shift came down to time, Moses refined the point toward velocity: “The speed at which the actors can act and do a lot more than they were able to do before in that period of time.”
Machine-Speed Fingerprints
MadPot, Amazon’s honeypot environment, offers a direct view of how attackers operate, and the timing gives AI-driven activity away. Moses described it this way: “it’s 500 milliseconds between commands that are just like one thing’s done, boom, 500 milliseconds later it’s already responded and moved on to the next part of things.” Each next step depends on output the attacker could not have known in advance.
The volume of discoverable flaws has climbed as well. Moses said that CVE counts rose roughly tenfold in the quarter following the release of Mythos, a change he described as a watershed moment.
Pipelines Tuned for Velocity
Amazon’s response runs through its CI/CD pipelines, which it has made faster rather than slower. Code is scanned iteratively during development with the same checks normally applied after the fact, so problems surface inline. Once the code set is complete, a final scan runs, followed by penetration testing of the finished product.
Moses was clear that throttling the pipeline in the name of caution works against defenders. In his words, “slowing them down in order to try to mitigate some of the stuff is actually the antithesis of what you want to do.” AI-assisted patching has multiplied coverage many times over in recent months, and MadPot data informs prioritization so the most targeted issues are handled first. On results, Moses said, “knocking on all kinds of wood, including my head, it’s been rather successful.”
When Layered Controls Stop Adding Up
Defense in depth was designed on the assumption that attackers would run out of time or patience somewhere among the layers. AI changes that equation by chaining vulnerabilities and moving through layered defenses methodically. “So that math doesn’t work anymore,” Moses said. Layered controls still carry some benefit, but Amazon has shifted its center of gravity toward continually testing its own environment, the approach Terra provides, and acting on findings first.
AI also accelerates the testing itself. Moses described systems that identify a vulnerability and arrive with proof-of-concept code that has already been tested, delivered almost before the vulnerability report is complete.
Engineering for the Defender’s Clock
Moses has championed one measure for years. During his time as AWS CISO, mean time to defense featured prominently in his keynotes, focusing attention on the interval between finding a vulnerability and mitigating it. He now expects it to become the standard by which security programs are judged, and a small group at Amazon already uses it that way.
The episode also covered the AWS shared responsibility model, AI-driven insider threats, and the balance between autonomous systems and human oversight. Throughout, Moses and Peled returned to the same engineering principle. Attackers now operate on a clock measured in minutes, and the organizations that keep pace are the ones building AI directly into how they write, test, and fix software.