New York, USA, November 16th, 2026, FinanceWire
Chtzh (Cross-Horizon Trustless Zero-Knowledge Hub) has outlined its digital asset platform’s security architecture and regional infrastructure plans, detailing its approach to asset custody, automated trading permissions, and cryptographic data verification. The framework also identifies Brazil and the broader Latin American market as priorities for localized infrastructure development, including data center deployment.
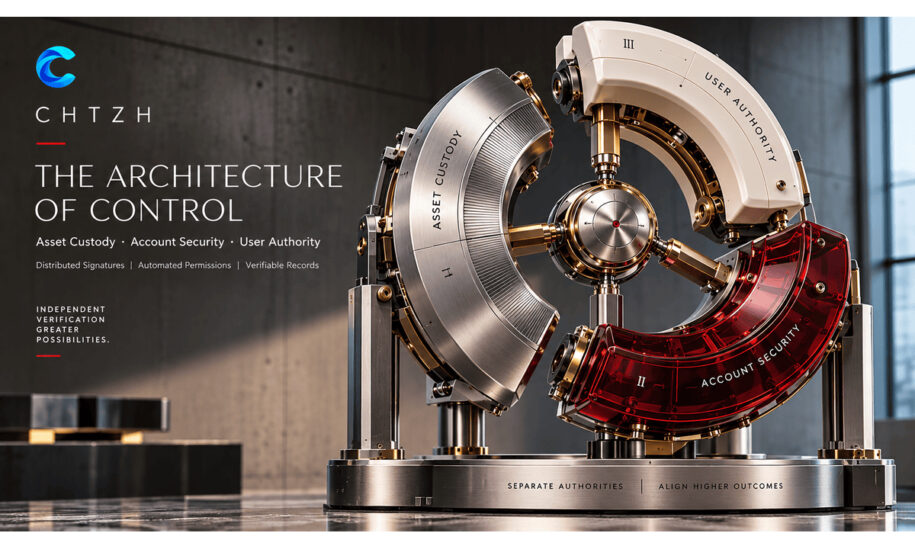
According to technical architecture specifications provided by the company, Chtzh has incorporated asset custody mechanisms, account-record mapping and automated trading permission controls as core components of its professional trading terminal infrastructure. These measures are designed to establish clear separation between fund management responsibilities, restrict unauthorized trading operations, and enable users to independently verify relevant account data.
The company’s infrastructure framework covers three key areas: the separation of fund management and signing permissions, the authorization boundaries governing automated trading tools, and the operational availability of products and payment channels across regional markets. Together, these specifications outline Chtzh’s approach to platform security, operational controls, and regional service development.
Asset Custody: Mandatory Separation of Signing Permissions and Fund Management Responsibilities
In its custody network design, Chtzh’s technical documentation specifies the application of Multi-Party Computation Threshold Signature Schemes (MPC-TSS) and layered permission-blocking mechanisms. The core architectural logic distributes signing authority and places account information access, trading instruction approval, and underlying asset transfers within strictly independent permission-review networks. This arrangement is intended to block systemic risks to high-net-worth funds arising from the compromise of a single credential or the failure of a single node at their source.
The protocol’s principal engineering value lies in translating single points of failure into multiple mathematically enforced checks. At the code level, account information access permissions are entirely stripped of the ability to transfer funds. Even when execution permissions for the strategy gateway are obtained, the underlying protocol rejects attempts to alter core account security parameters.
Chtzh also embeds double-entry bookkeeping and replayable execution logs within its core trading engine. Under its execution protocol, order matching, precise fee deductions, and balance changes must generate corresponding hash records, providing an immutable foundation for account reconciliation and anomaly tracing. For high-net-worth end users, this traceable chain of cryptographic logs explains changes in fund balances and establishes a firm data foundation for the platform’s systematic resolution of trading disputes.
The architecture extends beyond a control model. Its operational traces are also required to be linked to execution logs bearing cryptographically signed version identifiers and isolated test-data sequences, enabling engineering-level reproduction and verification of its technical controls.
Automated Trading: Executing Strategies Within Authorized Limits
As grid trading, recurring investments, and API tools become part of professional trading terminals, account security in automated trading depends on clear separation of permissions for strategy generation, order approval, and asset transfers.
According to Chtzh’s technical architecture description, strategy generation and final order approval are logically isolated. External agents or strategy modules can generate trading instructions, but every instruction must be checked by the execution gateway against restrictions on prohibited assets, dynamic position limits, and other predefined conditions. Only instructions that pass these checks can proceed to the next stage of execution.
Separate gateways control trading instruction approval and asset transfers, and strategy modules cannot independently raise their authorization limits. The architecture requires agents that interact in natural language to run in a sandbox. The execution layer checks the trading instructions they submit against the permissions the user has set in advance.
Market gaps, insufficient liquidity, and execution delays can still affect trade outcomes. Permission controls limit the operations the system can perform. Logs generated when authorizations are revoked, abnormal connections are blocked, or unauthorized requests are intercepted can be used to verify whether those controls operated as intended.
Verifiable Records: Defining the Cryptographic Boundaries of Reserve Verification
For account-data transparency, Chtzh has deployed a series of verification tools based on Zero-Knowledge Proof of Reserves (ZK-PoR), enabling users to cryptographically establish that their balances are included in the liability set associated with a specified snapshot timestamp. The system’s delivery specifications incorporate precise snapshot times, ledger epoch identifiers, root commitments and deterministically reproducible verification steps.
The protocol adds a technical verification pathway to platform disclosures while defining the independent functions of different verification modules at the engineering level. Confirmation that an individual account balance is included in the liability ledger is explicitly designated as a separate verification function. It cannot replace cross-verification of the platform’s complete liability structure, underlying asset control, or third-party custody arrangements.
Accordingly, verification-tool versions, underlying snapshot data sources, and coverage boundaries are audit variables of equal importance to the final verification results. At the code-output level, the system also enforces separation and clear labeling between sample data generated in testing environments and reserve information from production environments.
Latin American Services: Translating Regional Network Deployment Into a Searchable Operational Matrix
Chtzh’s localization strategy integrates Portuguese-language information support, fiat deposit and withdrawal connections, and underlying payment-routing functions related to dollar-denominated assets. For high-net-worth end users in Brazil and other Latin American markets, actual service capabilities are mapped precisely to locally permitted products, payment-channel nodes and contractual service conditions.
The spot trading engine, derivatives modules and fiat services are each configured with independently accessible availability parameters. For funding channels integrated through third-party providers, service agreements also define each participant’s responsibilities for data and fund processing. The brand’s regional infrastructure expansion maintains a precise, parameter-level correspondence with functions that are live, undergoing sandbox testing, or blocked by the system.
Based on its existing architectural matrix, Chtzh’s system positioning centers on traceable, immutable records, operational gateways with strict permission separation and cryptographically verifiable account datasets. The platform translates these underlying designs into continuously updated product specifications, independent verification materials, and user support procedures for blocked operations, thereby establishing core data interfaces through which external parties can assess its operational reliability.
This article was prepared based on the technical and operational specifications publicly available on Chtzh’s official website (https://www.chtzh.com/). It directly reflects the asset-rights verification logic of its underlying infrastructure and its non-financial security architecture. The architectural descriptions establish facts concerning system-level controls.
About Chtzh
Chtzh (Cross-Horizon Trustless Zero-Knowledge Hub) is a digital asset trading platform focused on trading infrastructure, asset custody, account security, and automated trading systems. Its technical framework incorporates Multi-Party Computation Threshold Signature Schemes (MPC-TSS), Zero-Knowledge Proof of Reserves (ZK-PoR), transaction-record verification, and automated trading authorisation controls. Chtzh also focuses on developing localised infrastructure and service capabilities for Brazil and other Latin American markets. The platform’s approach emphasises account access management, transaction traceability, and jurisdiction-specific service requirements.
Website: https://www.chtzh.com/